Optimizely supply‑chain attack compromises 178 major websites
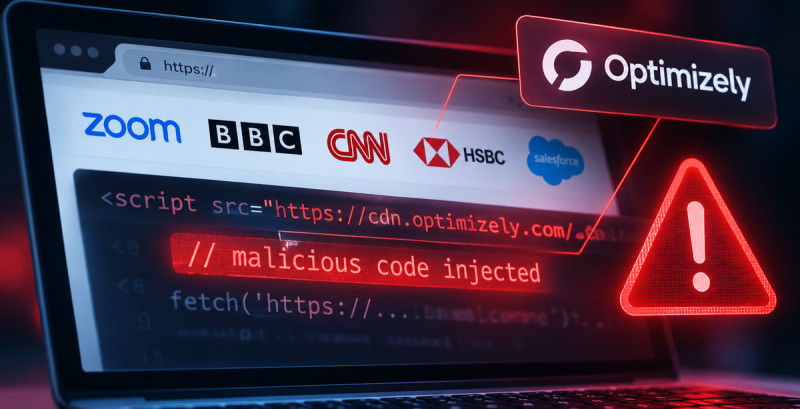
Malicious JavaScript injected into Optimizely’s CDN on Nov. 16 reached visitors of 178 sites, including Zoom, BBC, CNN, and Salesforce, stealing data and pushing exploit kits.
Key points
- Attackers inserted malware into Optimizely’s Project JavaScript field on Nov. 16.
- The code served from cdn.optimizely.com swapped crypto wallet addresses, stole payment card data, captured cookies and screenshots, and pushed exploit kits to iOS devices.
- Cryptocurrency was stolen and traced to attacker‑controlled wallets.
- Optimizely had not issued a statement and the method of platform access remains unknown.
- Most malicious code was removed by Monday evening UTC.
Attackers planted malicious JavaScript inside the Optimizely Web experimentation platform on November 16, 2026, compromising the sites of 178 organizations. The malicious code was served from Optimizely’s content delivery network and reached visitors of major brands, including Zoom, the BBC, CNN, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM, Ledger, and Peacock.
Multi-Purpose Malware Kit
The malware functioned as a multi-purpose kit rather than a simple skimmer. It swapped cryptocurrency wallet addresses, stole payment card details from checkout forms, grabbed cookies and screenshots, and pushed the Coruna and DarkSword exploit kits to iPhone and iPad users. Researcher Scott Helme of Report URI confirmed that cryptocurrency had already been stolen and traced the transactions to wallets controlled by the attackers.
The attack exploited a trusted third-party script loaded on every page of the affected websites. Optimizely Web allows customers to load a JavaScript snippet from cdn.optimizely.com, which includes an optional field called Project JavaScript. The attacker wrote a small loader into this field in many unrelated customer projects, leaving the rest of the snippet untouched. Because the file was served from Optimizely’s domain with its certificate, browsers and security tools treated the code as legitimate.
Removal and Investigation
Most of the malicious code was removed by Monday evening UTC. Report URI detected the malware in 169 infected snippets at 20:56 UTC and in only one, TalkTalk's, at 21:52 UTC. The method by which the attacker gained access to the platform remains unknown, and Optimizely had not published a statement at the time of reporting.
Your questions, answered
Which sites were affected by the Optimizely attack?
The attack compromised 178 organizations, including Zoom, BBC, CNN, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France‑KLM, Ledger, and Peacock.
What did the malware do?
It swapped crypto wallet addresses, stole payment card details, captured cookies and screenshots, and pushed the Coruna and DarkSword exploit kits to iPhone and iPad users.
How does this story make you feel?
Topics
 Up next · TechNvidia shares fall 4% as markets slide before earnings release